Clojurians Log v2
web-security 2017-03-01
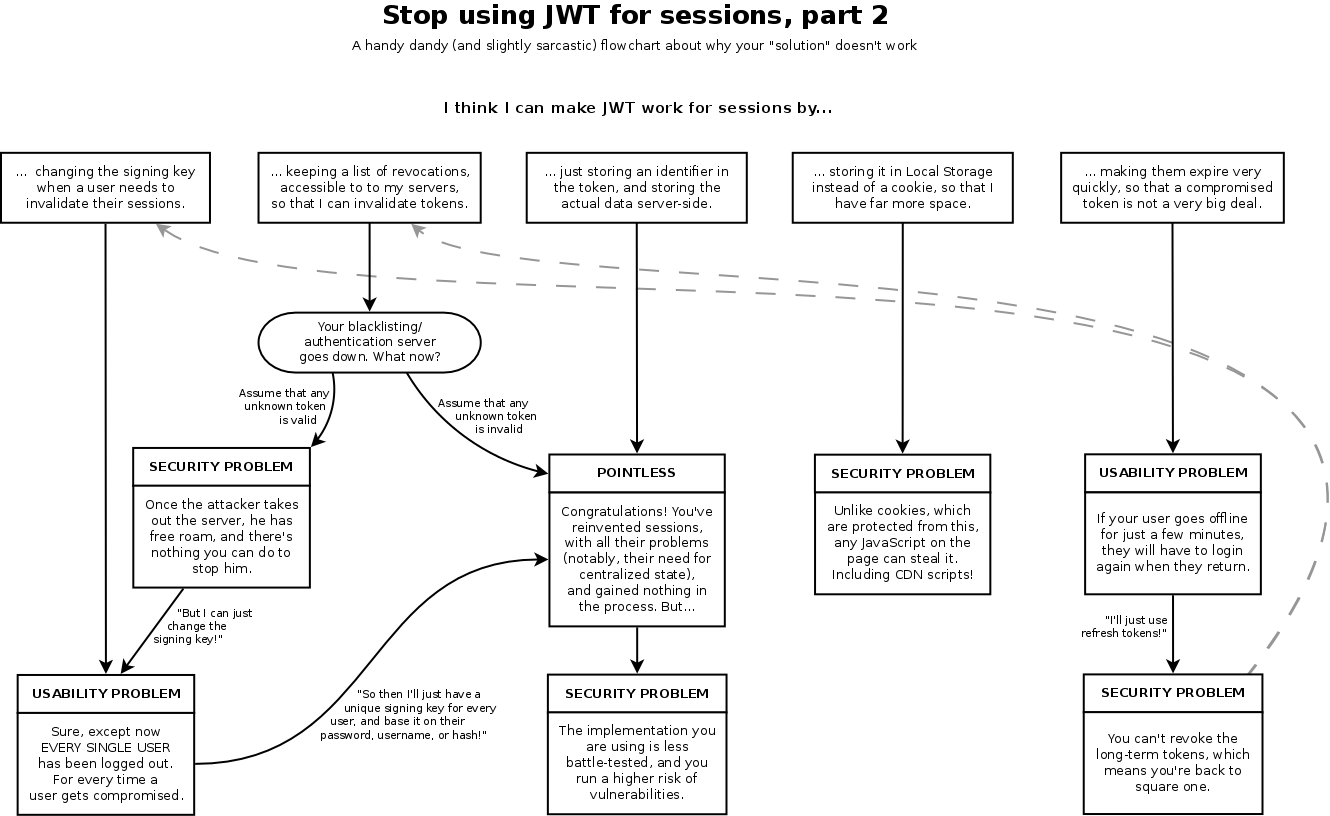

I think the default recommendation would be to not recommend JWT for sessions.
"I emphatically recommend that you not use JSON web tokens for a security problem as straightforward as protecting an API. JWT is a horrible kitchen-sink standard; it is cryptographically terrifying. 99 times out of 100, the problems people try to solve around APIs with cryptography are better solved with simple 256-bit random integer tokens." https://news.ycombinator.com/item?id=9619902
Note that sending and saving session data via cookie or other means (local storage) is a different manner.
In that respect, local storage might even be better, according to: http://blog.portswigger.net/2016/05/web-storage-lesser-evil-for-session.html
I suggest for security and flexibility purposes to front your users from a single server (which does auth and proxy to other servers). JWT might be used for collaboration between the services behind that proxy. In this way, you don't hard-code the services in your users app, and can change their locations at will.